Thread · 7 tweets · 23 Jun 2023

It's hard to capture just how much of a catastrophically broken crock of shit @MicrosoftTeams is. If your organisation depends on interacting with people who aren't locked into a Microsoft-managed intranet, I strongly encourage you to migrate away.
It's not the first time I've been locked out of a meeting because of Teams, and I know it's a common experience for many of you, but banging on it to make it work shows just how baroque and brittle the implementation is. The app? Endless login dance, then stuck on this:
It doesn't matter that I've used the app before, logged in with that account before, it wants to know if this is for personal use — which is the only option in the drop down anyway. Sometimes you get this full screen, sometimes in a popup that pops under on submit, does nothing.
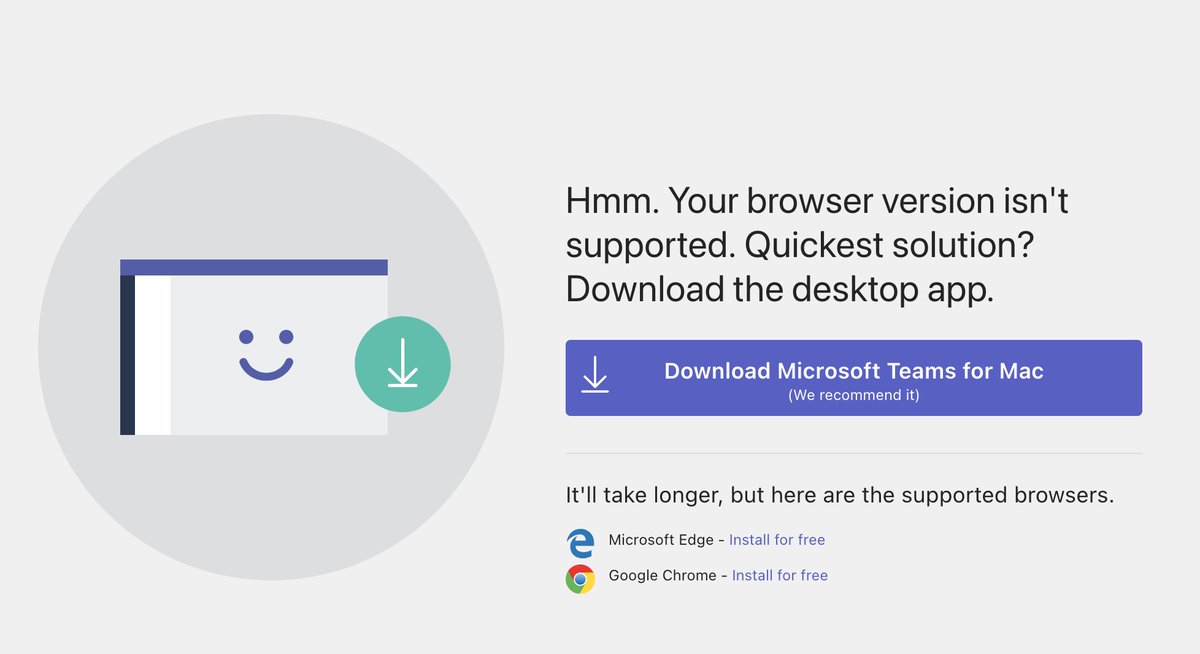
Web version? Another (but different — it's all over the place) lengthy very slow-loading login dance with a million redirects and… oh it doesn't work on the latest Firefox. Forget the fact that this is amateur-grade web development work, they knew this *before* the login dance.
Two more attempts (always with trawls through various login flows — I think they're longer even than those that Yahoo! had fifteen years ago) eventually land me on some useless chat and calendar thing, all empty — but not my meeting.
Anyway, the take-away message is this: I know that enterprise security is often this bad. But I don't believe that it's possible for something that's obviously built in such a haphazard way to be secure. I don't believe that a diligent CISO would tolerate Teams.