May 2018
158 tweets
Most of the time yes, but not always. I can see a number of cases in which consent is called for, but it should be local and overwhelmingly clear why (eg. a direct survey involving sensitive data). In all other cases I would assume you’re doing sth not in the user’s interest.

Not everything (there is still a lot to put under contractual) but a lot.
I think that’s a point of disagreement right there: I would want to carry out a balancing test (even if very basic in some cases) for pretty much any personal data processing. I don’t see how you can approach privacy user-first without it.
I did not say "usually". My strictly personal appraisal is that it is possible to carry out advertising that does not threaten personality integrity through inappropriate flows of personal information, including up to extremely limited behaviour (very coarse).
♥ 1
Given sufficiently limited risks to data subjects and the necessity of ads in some business models I believe it possible to find this falling under legitimate interest.
♥ 1
Now as to the behavioural targeting in full regalia, my own view is that it would indeed require consent because of how comprehensive it is and how much sensitive data is involved, but since consent is only valid if informed I would contend that it only holds if...
♥ 1
...you regularly show the user how exactly you've profiled them and who has seen that profile. Otherwise it's too opaque. I stand by my recommendation: do not consent unless it's evidently OK.
Would you disagree?
I'm curious: has anyone actually audited the level of ad fraud on Facebook that may be driven through such bots?
Quoting a tweet by @CraigSilverman ↗
♥ 4
It is hazy, that's why I think it's useful to discuss. A lot of the aspects involved are quite subtle and complex.
♥ 2
Retargeting is indeed a complicated case. I would tend to say that ITP-level retargeting (you have 24h within which to recognise a user) could be fine, again because of the limited scope. But that’s really up for discussion.
♥ 1
They’re not asking for consent for participation in their ad network, they’re asking it for profiling. That’s the differentiating factor. Web-wide profiles are terrifyingly precise and quite invasive. I would rate that as problematic even if no targeting or ads were ever shown.
To put things differently, to me the targeting is almost immaterial. If you could come up with a way to target me super-specifically without ever building a profile that might be okay. The profiling is the problem — even if you’re not using it for targeting.
But I may be somewhat heterodox in that assessment.
Indeed. Maybe crazy idea: if I were a FB shareholder I would be terrified of massive fraud being uncovered and leading to massive stock/revenue tailspin. Could those folks force FB into third-party auditing here? Cc @jason_kint .
Thanks Jason, that's very interesting to hear!
"What Is Real?", by @FreelanceAstro. An unforgiving history of 20th century physics. In many ways it is reassuring to see the pettiness and failings of science giants rather than the usual hagiographies. Well-worth reading!
♥ 5↺ 1
I can't even begin to estimate the depreciation in ad pricing from having such a behemoth let bots run free.
♥ 1
I often consider that too, but it feels pretty hard to get into and most people I know there tell me to run the hell away.
♥ 1
"Visual Group Theory", by Nathan Carter. I had to wait months to find an affordable copy but I'm glad I did. It's a model of high clarity that mathematical texts could emulate.
Only two gripes:
- $500 is not a sane price @maanow
- many exercises do not have solutions.
♥ 8
You know… it might not be the craziest idea to have mini InfoSec people sitting on people’s desks everywhere, watching :)
♥ 2
That's the price I eventually paid, but for some months before it was listed in online stores at $4-500 prices. Was it out of print for a while? Anyway I'm happy to find out that's not the case!
♥ 1
I've been wondering if it wouldn't make sense to build an SVG tool that sort of marries both aspects, sticking to code principles but making it a bit more visual (especially paths).
♥ 8↺ 1
Le travail?
I don't think that not wanting to be next is the primary driver for this happening behind closed doors, most companies I've spoken to don't believe they have data practices that resemble FB's. A big driver of silence is people not knowing what's right, what's ethical.
♥ 1
Privacy feels fuzzy to many, it's the kind of concept that engineers have too often (wrongly) shunned because it feels philosophical. Now the class doesn't want to speak up because they haven't done their homework.
I don't agree with everything that Brad says in this thread but I am thankful that he posted it. It's a bunch of conversations we need to have.
Quoting a tweet by @hillbrad ↗
♥ 2
If there are opportunities for feedback I’d love to look at drafts and the such!
♥ 1
#GDPR teams in companies the world over this month. youtube.com/watch?v=-qTIGg…
At this point stage I'd recommend Public Interest.
♥ 1
After reading this article I feel that the US/EU cultural difference on the right to be forgotten is less about freedom of speech and much more about a passion retributive justice and ridiculously cumulative sentencing.
Quoting a tweet by @nytopinion ↗
♥ 3
I am considering a Letter. I'm still deciding if that makes me opinionated or just old.
♥ 1
Agreed, I avoid using a browser for real work as much as I can because of that. I'd like to be able to have a domain participate in cmd-tab, that sort of thing.
Yeah — you can blame me for the schema.org stuff in there ;-) And we should definitely talk more often! That paper even belongs to a completely different life, I don’t even work on that anymore!
I know, but there was a lot of initial push back against that for some reason. Come to New York!
The oil industry replaced the whaling industry so you have an exciting improvement right there.
Alas no but maybe we could curate one together!
Hahaha that’s brilliant!
Je ne sais pas, il faudrait demander à un Parisien en fait ;-) Peut-être que @versac ou @_nemodemo ont une idée?
♥ 1
I came away from a school event last night with a voucher for a tattoo parlour…
Design it for me Twitter!
♥ 1
Good choice — saw it coming but good choice :)
♥ 1
I’m not sure the voucher covers that :)
Or my most important retweeted tweet?
Ooooh interesting!
It may be considered an improvement over @danbri's 😉
That's beautiful. The problem is that I don't have meaningful visual things like that!
You're way too hardcore for me, I don't think I could go THAT far!
♥ 1
The American and French presidentials of 16-17 almost got the better of me.
♥ 1
I was actually just trying to draw attention to its wonderful content for anyone who might not have seen it yet 😀
♥ 1
I could just go with <rb> as a more personal touch.
♥ 6
Yes, IIRC it's the same roots as French tu/vous.
♥ 1
Not enough knuckles 😋
My 8yo wants "a sciency birthday party" when she turns 9 next month, in the New York area. Any recommendations?
♥ 1↺ 1
Sorry if it wasn't clear! Never gonna tell a lie and hurt you!
Is it really good? We haven’t been yet (I mean, it’s in a whole other state and all) but if it’s really good we could hop over the Hudson.
Putain, ils se sont payé un TLD .sncf mais ils ne savent toujours pas faire un site rapide avec des formulaires qui marchent. 🤦🏼♂️
♥ 12↺ 3
Thanks, I'll look into it! Wait, you were on this coast little?
Stares.
♥ 1
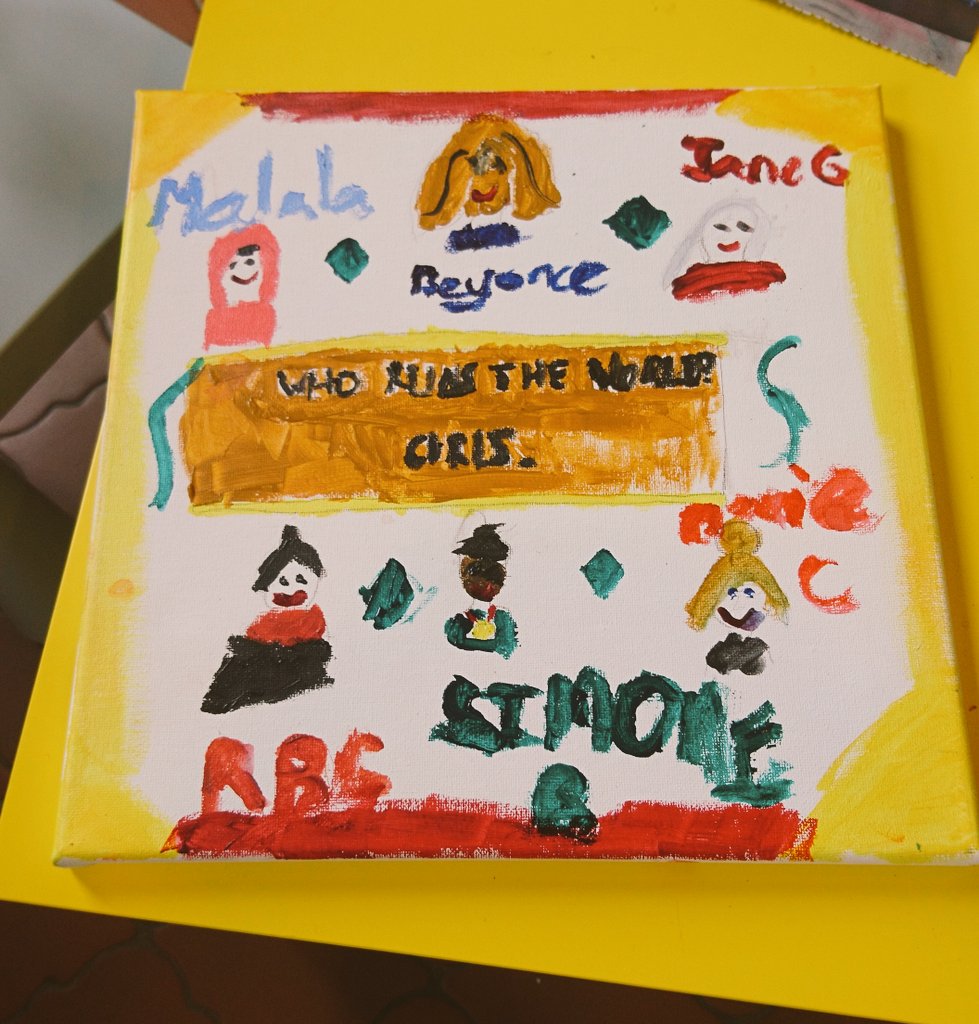
Malala, Beyoncé, Jane Goodall, RBG, Simone Biles, Marie Curie. I'd say that's a pretty damn good pantheon to pick 😊 #WhoRunsTheWorld
♥ 7
The crazy things you learn about people on twitter!
Je connais quelques gens qui peuvent te faire un site pour juste un chèque!
Ça m'est arrivé dans un train de banlieue à Tokyo. On est passé très très près de dormir dehors!
♥ 1
Classique. Une fois j'ai voulu rentrer à pied de Barbès à Ménilmontant "pour m'éclaircir les idées". J'ai réussi à tourner dans le mauvais sens au canal, j'ai découvert un beau bout d'Île de France avant de m'en rendre compte...
♥ 1
For trains yes, but not for planes.
It's not great but it sucks less than most alternatives I've tried.
♥ 1
C'est ultra lent et souvent inutilisable au clavier.
Ah oui? J'avais essayé il y a longtemps, il y avait une espèce d'agent automatique mais dès qu'on décrivait un problème avec le site ça se bloquait 😂
- Do you really expect me to fix the Bluetooth pairing with one hand and a drone in my face?
- No Mr. @torgo, I expect you to die.
♥ 2
If you figure out a way of reading while running I might finally get started running. The idea of just throwing one's legs around all that time without anything to do is not easily contemplated.
♥ 1
Audiobooks and podcasts never worked for me, it's like they slip through my brain and leave no trace. Maybe I should get a treadmill indeed 😱
♥ 1
Having fun with the #GDPR already? Here’s what the proposal to bring similar regulation to California this November looks like. (I’d vote Yes, follow @caprivacyorg for more):
mofo.com/resources/publ…
♥ 4
One thing that’s annoying with @caprivacyorg though is that they seem to have adopted terminology arbitrarily different from the #GDPR for no good reason. We already have a hard time telling people about PII vs personal data, throwing “PI” into the mix won’t help.
Seriously, I hope someone figures out a way of keeping The Expanse alive; it’s easily one of the best scifi shows in a long while. #SaveTheExpanse
♥ 6
You know we have open positions, right? 😇
Ha! C'est presque tentant 😀 Mais la fiche de poste ressemble un peu à des vacances où tu t'ennuies au bout de quelques jours, non?
I take it he’s speaking in favour of drug decriminalisation?
Asking for consent to personal data processing feels a lot like a revival of the ActiveX security model: abdicate responsibility by punting to the user without it being possible for them to make a sufficiently informed decision. #GDPR
♥ 3
Put differently, in the context of modern data processing, relying on consent for the #GDPR is like asking people if they want to leave the European Union: you'd better be damn sure they understand their best interest before popping up the question.
♥ 2↺ 1
La Caaaa-liiiii-forniiiiiiiiie!
♥ 1
HAHAHA, OMG that’s just perfect :-D
Question to all you #GDPR friends: users do not know their browsers are sharing tracking data with third parties, and certainly don’t instruct them to do so.
So, under what legal basis are browsers sharing that data?
♥ 1↺ 5
Great @nytopinion from @SenBlumenthal and @superwuster: “What the Microsoft Antitrust Case Taught Us”. We need much more serious antitrust enforcement. nytimes.com/2018/05/18/opi…
♥ 1
They write that “there is now no browser monopoly”. I’m afraid however that that statement is decreasingly true:
netmarketshare.com/browser-market…
↺ 1
?
It is now safer for American children to enlist with the military than to go to school. #VoteThemOut
Quoting a tweet by @dabeard ↗
♥ 3↺ 3
Écoutez absolument cette vidéo sur l’accès qu’ont les personnes qui écoutent vos conversations avec les assistants vocaux pour débugger leurs IAs. En clair: à tout, sans contrôle. Édifiant.
Quoting a tweet by @AntonioCasilli ↗
♥ 18↺ 17
Le "Coup de soleil" de Richard Cocciante n'est pas sur Spotify. Aidez-moi, qui faut-il contacter? L'Académie Française? @EmmanuelMacron?
♥ 3
I know! It's hilarious! Seriously though, do you reckon this could hold water in court? I can't find a reason why not. Sites that call third parties are under at least transparency requirements, why not browsers?
This really makes me wonder how solid Google’s #GDPR project is.
Quoting a tweet by @davemethvin ↗
♥ 5↺ 1
Given how busy Facebook is repeatedly shooting itself in the face, they sure have a shot.
♥ 1
I just found out he has a new book, can't wait to read it!
♥ 2
Except that if it blocked anything someone at DoubleClick would realise that jQuery has zero actual GDPR exposure and rescind that request. I expect to see some fireworks, but not this one!
♥ 1
For libs, the risk is almost null since they aren't controllers of the data, acting independently. I could imagine a complex & poorly documented system getting in the way of transparency obligations, but it's a stretch.
Openness of source shouldn't be a factor, I would think. I believe there is a case against browsers since they misbehave with user data in ways that benefit their parent companies. But I won't be checking my own open source stuff for compliance!
That’s a good case; and as often with the GDPR it will boil down to reasonableness and proportionality. The dev is almost certainly off the hook, unless it’s actually their business, they’ve made false claims, have been shockingly bad, etc.
For corporate users of open source, yes, this does lead to a responsibility to check that they’re using good stuff. But again, it will boil down to specifics. If your whole data rights strategy hinges on a broken anonymising function that you didn’t check, you’re toast.
♥ 1
But if you suffer a breach for zero-day in a dependency seven layers down in npm, I don’t think anyone could possibly hold it against you.
The GDPR is basically good housekeeping.
♥ 1
Google essaie de faire porter le chapeau de ses traitements de données personnelles aux éditeurs. @ElisaBraun couvre la grogne.
lefigaro.fr/secteur/high-t…
GDPR really isn't checklist compliance so I'm really playing judge/regulator here but: the facts matter most. If the software presents no risks to the rights and freedoms of data subjects you're OK no matter what whoever says.
If however it's problematic software AND you were warned, you're going to have a bad day. There's a good example of the sort of thinking we expect for enforcement in blog.lukaszolejnik.com/everything-you….
I'm all for revolution and I've been steeped in the GDPR for months, happy to help look for a way! If you're in the area early June, we're planning a small gathering to annoy capitalism with GDPR rights. 🔥
♥ 1
If capitalisation is dead on the morning of June 5th you'll know why!
Capitalism, though capitalisation might take a hit.
Probably worth knowing: if you get scammed online (eg. purchasing something and getting an evidently fraudulent knock-off) you'll be much more protected if paying with a card than through @PayPal. And that's saying a lot.
♥ 2
Ça me rappelle une amie qui, voulant indiquer qu'elle était célibataire, dit "I'm celibate".
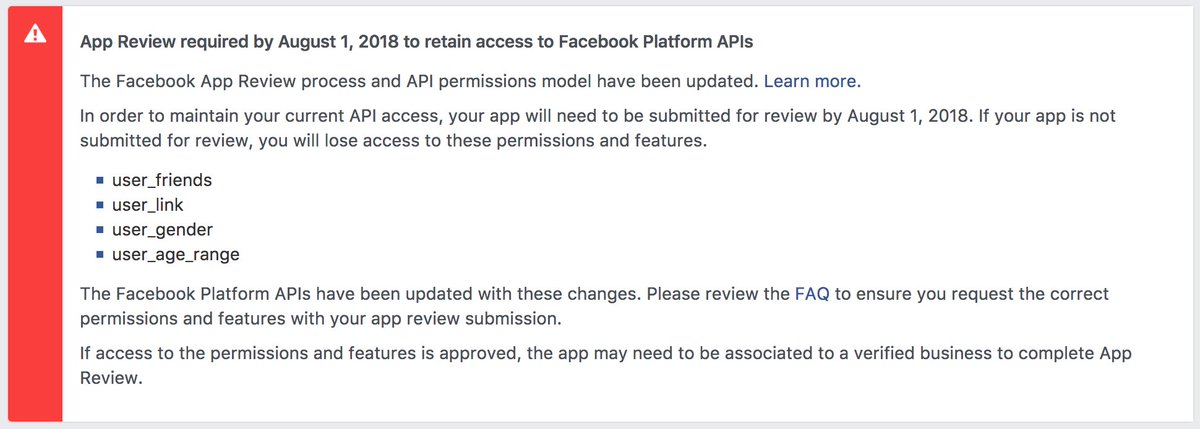
Right now Facebook just throws your gender, age range, and a bunch of other things at sites that use their social login solution.
You should just never use them, but at least later this year this’ll require review.
Thank you #GDPR!
♥ 9↺ 1
I... I think I want one.
♥ 3
That's genius. Just pure genius.
♥ 2
WORD
♥ 1
I sense a Unicode proposal in the making.
Quoting a tweet by @existentialcoms ↗
It's one of the things I actually find most useful at conferences: finding out how all those words (and names!) are pronounced.
Yeah, it’s so private you’ll never find it again.
I personally find the search dreadful, I usually have to go into email or Slack logs to find my documents again; but YMMV.
♥ 1
Stilton. And it's so good I'm not sure it's debatable.
♥ 1
Two lightbulbs.
I’m so excited that the #GDPR is coming into effect it’s ridiculous. #PrivacyNotDead
♥ 7↺ 1
What do you get for that special person in your life who already has a "Carpe Diem" tattoo?
Wow! Well done old friend!
Agreed, the ability to state that two domains are jointly owned and operated could open the door to useful stuff.
♥ 1
The question is not whether people prefer relevant ads, it's what they are willing to trade in exchange for relevant ads. Those two things are very different.
I'd be curious to see what you consider counts as showing people what you track. The data export for instance does not have that, neither do the privacy or ad settings.
Privacy's back, folks! And she's pissed. #PrivacyNotDead
♥ 5↺ 1
OMG we are so little!!!
♥ 3
But that hasn't changed.
♥ 2
The absurd thing with this #GDPR hysteria is that shuttering your website in Europe does not absolve you of responsibilities. If you still have database on European residents you're still on the hook.
As a regulator I would go after these *first*! politico.eu/article/gdpr-h…
♥ 33↺ 22
That's almost true, but revenue will likely be affected some, at least temporarily.
The WaPo's take is certainly interesting. I don't know if this holds water as freely-given consent (or informed, for that matter, given that it's all bundled) but I'm curious to hear if it works!
Quoting a tweet by @adrianweckler ↗
♥ 2
I really don’t understand how Google planned its GDPR project. I don’t know if it’s hubris or arrogance or being too big to change nimbly, but the strategy of their ad business has seemed haphazard at best throughout. digiday.com/media/gdpr-may…
♥ 1
Same method as @fantasai for me. It's not great but people can mostly read me now.
Is this the @nytimes one?
Please do it, I want that in the learning review that I'm already setting up.
♥ 14
I'd be much obliged.
I'm trying to get it plugged, though, so it might not work 🏃
♥ 7
We just plugged the issue so I'm afraid the fun's over!
♥ 8
It should be fixed now, sorry about that!
♥ 2
Maybe we can use that for the apology I think we'll have to write 😇
♥ 5
Those are somewhat different issues, though. When you publish something it’s at least obvious that it is being deliberately shared (even if the degree might not be fully grasped). Most online privacy issues are through behavioural tracking and such, where people have no idea.
I've had to make things point many times over, and more often than I'd like to people whose job it was to know. I'm not sure how we got here.
Il n’y a pas une formule abonnement pour les Notes de @Bouletcorp? Ceux d’entre nous qui habitent de lointaines terres d’aventures ne voient pas les traditionnelles 4x3 dans le métro ni n’entendent les annonces co-brandées Leclerc sur Nostalgie.
The worst part is that most of those emails were likely not needed but rather CYA thinking. But I’d take those again too!
Plus the amount of crap I filtered from it is amazing.
Ah, ils ne font pas ça? Peut-être que depuis l’étranger on idéalise certaines choses :)
Many did, but many didn't. There's definitely value to be had from an American GDPR. I'd say look at @caprivacyorg!
♥ 1
I... What?
♥ 1
Man, I need that shirt.
♥ 3
Quoting a tweet by @mikarv ↗
♥ 5↺ 2
The whole thing! I completely agree with him, yet I feel for our British brothers and sisters.
I like @superwuster’s idea in “An American Alternative to Europe’s Privacy Law” that data regulation should revolve around fiduciaries, but that is in effect a lot of what the #GDPR does. It is not a compliance checklist regulation — at all. nytimes.com/2018/05/30/opi…
♥ 2
In fact, that’s what a lot of people have found difficult with it. In some ways it is a set of guidelines with no precedents to guide expectations. The way I’ve been conveying this is about “being trustworthy custodians of our users’ data”: basically fiduciary duties.
People fear regulators, but I expect a certain proportion of the actual content of the #GDPR to be set in court. Lawsuits have already kicked off, we’re going to see some large aspects litigated.
says: “the European approach runs the risk of being insensitive to context and may not match our ethical intuitions in individual cases.” I would be curious to see an example of where that might happen.
♥ 1